
[2021] Use Valid NSE7_EFW-6.4 Exam - Actual Exam Question & Answer
Test Engine to Practice NSE7_EFW-6.4 Test Questions
How to book the Fortinet NSE7_EFQ-6.4: Fortinet NSE 7 - Enterprise Firewall 6.4 Exam
Follow the steps below to register for the Fortinet NSE7_EFQ-6.4: Fortinet NSE 7 - Enterprise Firewall 6.4 Exam:
- Step 1: Visit Fortinet’s website from here
- Step 2: From the panel on the right, click “Book the Exams”
- Step 3: Scroll down and click the register option
- Step 4: Create your account on the website, log in if you already have one
- Step 5: Select your exam, i.e., NSE7 EFW-6.4 exam test
- Step 6: Pay and schedule your exam
- Step 7: Buy NSE7 EFW-6.4 dumps pdf and take NSE7 EFW-6.4 practice test
For more info read reference:
Exam Blueprint Preparatory Course
NEW QUESTION 27
View the global IPS configuration, and then answer the question below.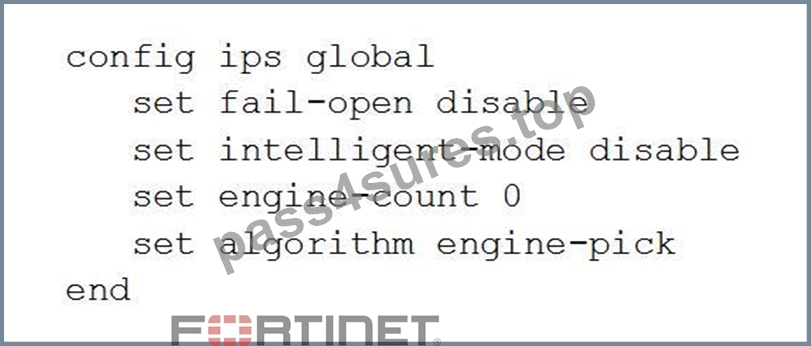
Which of the following statements is true regarding this configuration?
- A. New packets will be passed through without inspection if the IPS socket buffer runs out of memory.
- B. FortiGate will spawn IPS engine instances based on the system load.
- C. IPS will use the faster matching algorithm which is only available for units with more than 4 GB memory.
- D. IPS will scan every byte in every session.
Answer: D
NEW QUESTION 28
A FortiGate has two default routes: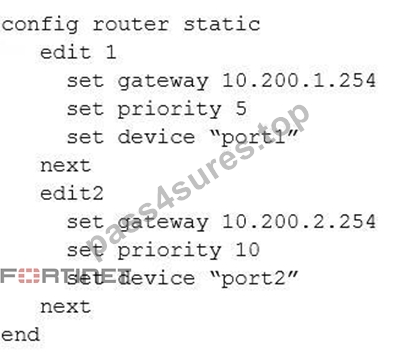
All Internet traffic is currently using port1. The exhibit shows partial information for one sample session of Internet traffic from an internal user: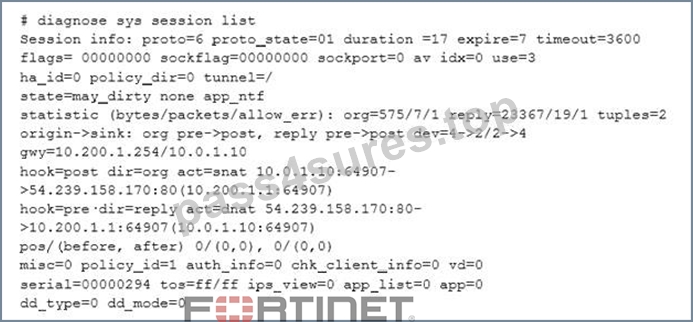
What would happen with the traffic matching the above session if the priority on the firstdefault route (IDd1) were changed from 5 to 20?
- A. Session would remain in the session table and its traffic would start using port2 as the outgoing interface.
- B. Session would be deleted, so the client would need to start a new session.
- C. Session would remain in the session table and its traffic would be shared between port1 and port2.
- D. Session would remain in the session table and its traffic would keep using port1 as the outgoing interface.
Answer: D
NEW QUESTION 29
View the exhibit, which contains the output of a web diagnose command, and then answer the question below.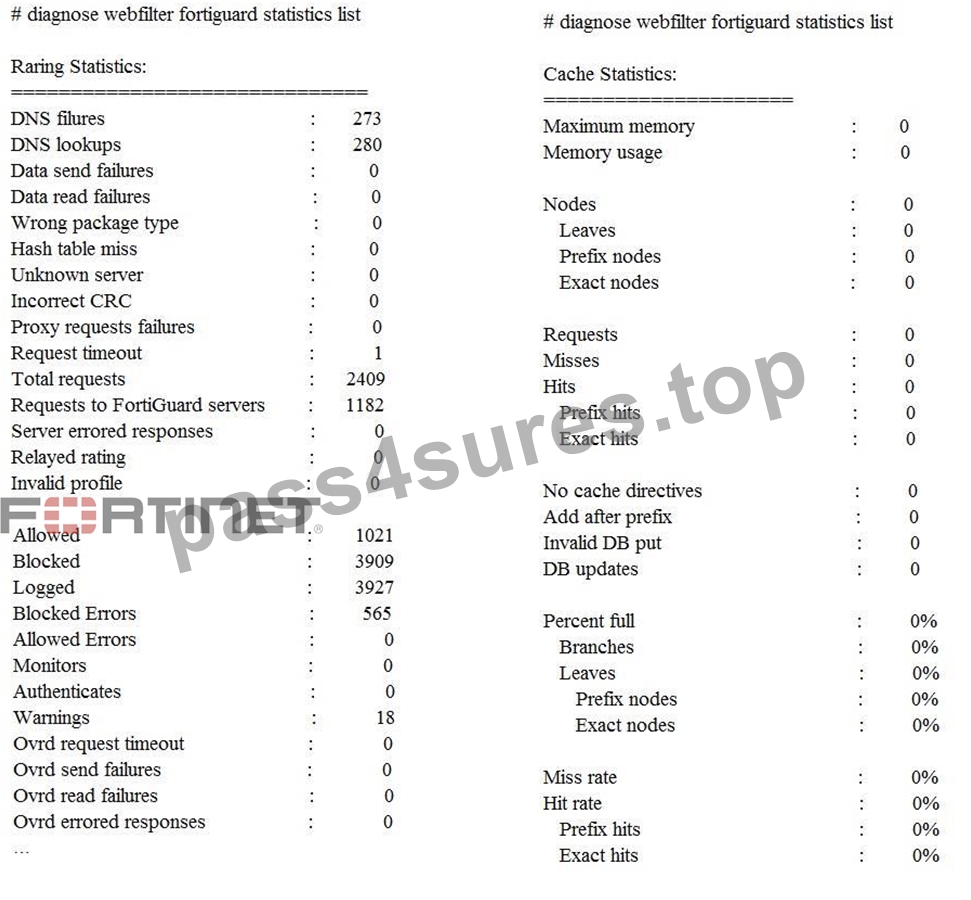
Which one of the following statements explains why the cache statistics are all zeros?
- A. The FortiGuard web filter cache is disabled in the FortiGate's configuration.
- B. FortiGate is using a flow-based web filter and the cache applies only to proxy-based inspection.
- C. Theadministrator has reallocated the cache memory to a separate process.
- D. There are no users making web requests.
Answer: A
NEW QUESTION 30
An administrator has configured two FortiGate devices for an HA cluster. While testing the HA failover, the administrator noticed that some of the switches in the network continue to send traffic to the former primary unit. The administrator decides to enable the setting link-failed-signal to fix the problem. Which statement is correct regarding this command?
- A. Sends an ARP packet to all connected devices, indicating that the HA virtual MAC address is reachable through a new master after a failover.
- B. Disables all the non-heartbeat interfaces in all the HA members for two seconds after a failover.
- C. Sends a link failed signal to all connected devices.
- D. Forces the former primary device to shut down all its non-heartbeat interfaces forone second while the failover occurs.
Answer: D
NEW QUESTION 31
What is the diagnose test application ipsmonitor 99 command used for?
- A. To restart all IPS engines and monitors
- B. To provide information regarding IPS sessions
- C. To disable the IPS engine
- D. To enable IPS bypass mode
Answer: A
NEW QUESTION 32
Examine the output from the BGP real time debugshown in the exhibit, then the answer the question below: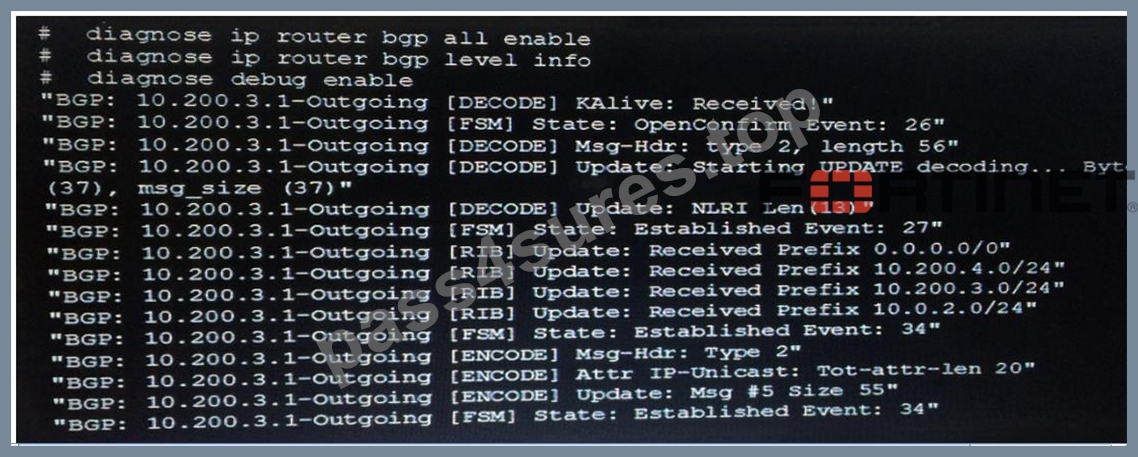
Which statements are true regarding the output in the exhibit? (Choose two.)
- A. The state of the remote BGP peer will go toConnectafter it confirms the received prefixes.
- B. Local BGP peer received a prefix fora default route.
- C. The state of the remote BGP peer isOpenConfirm.
- D. BGP peers have successfully interchangedOpenandKeepalivemessages.
Answer: B,D
NEW QUESTION 33
View the exhibit, which contains a partial routing table, and then answer the question below.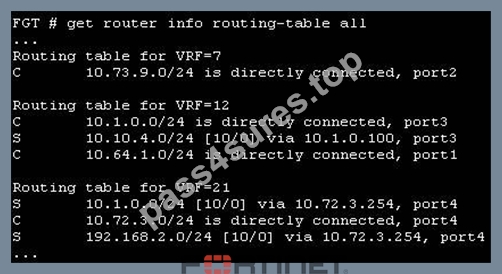
Assuming all the appropriate firewall policies are configured, which of the following pings will FortiGate route?(Choose two.)
- A. Source IP address10.73.9.10, Destination IP address 10.72.3.15.
- B. Source IP address 10.72.3.52, Destination IP address 10.1.0.254.
- C. Source IP address 10.72.3.27, Destination IP address 10.1.0.52.
- D. Source IP address 10.1.0.24, Destination IP address 10.72.3.20.
Answer: B,C
NEW QUESTION 34
When using the SSL certificate inspection method to inspect HTTPS traffic, how does FortiGate filter web requests when the client browser does notprovide the server name indication (SNI) extension?
- A. FortiGate uses the CN information from the Subject field in the server certificate.
- B. FortiGate blocks the request without any furtherinspection.
- C. FortiGate switches to the full SSL inspection method to decrypt the data.
- D. FortiGate uses the requested URL from the user's web browser.
Answer: A
NEW QUESTION 35
View the exhibit, which contains a partial web filter profile configuration, and then answer the question below.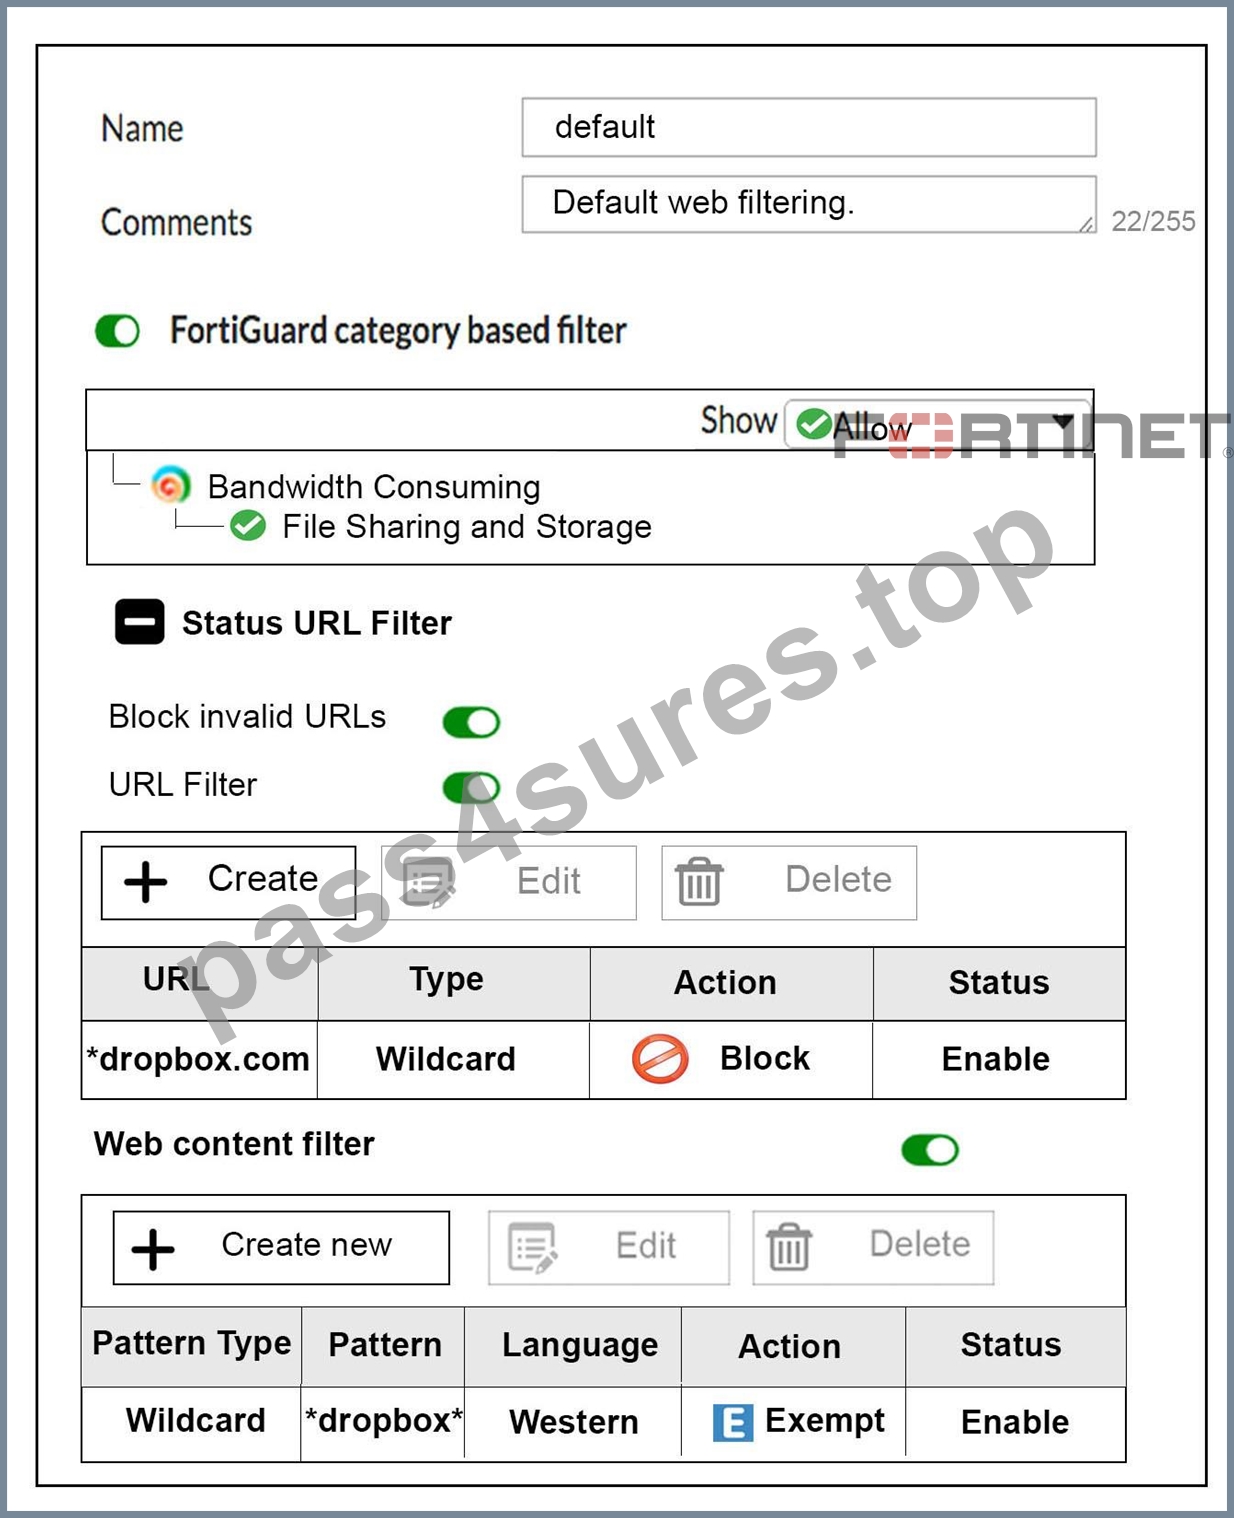
Which action willFortiGate take if a user attempts to access www.dropbox.com, which is categorized as File Sharing and Storage?
- A. FortiGate will block the connection as an invalid URL.
- B. FortiGate will exempt the connection based on the Web Content Filter configuration.
- C. FortiGate will block the connection based on the URL Filter configuration.
- D. FortiGate will allow the connection based on the FortiGuard category based filter configuration.
Answer: C
Explanation:
Explanation
fortigate does it in order Static URL -> FortiGuard -> Content -> Advanced (java, cookie removal..)so block it in first step
NEW QUESTION 36
Examine the following partial output from two system debug commands; then answer the question below.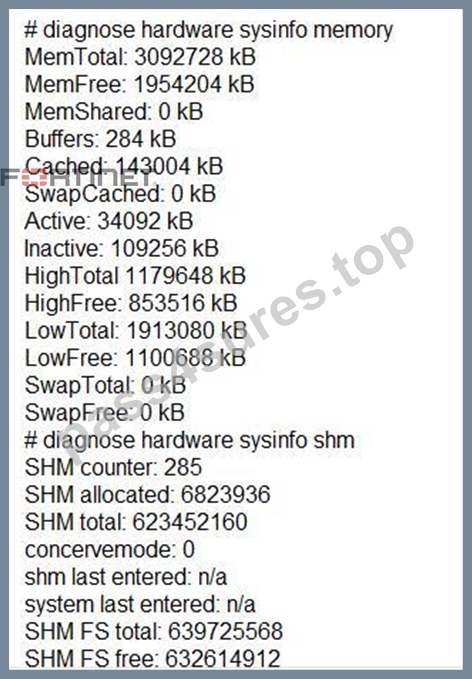
Which of the following statements are true regarding the above outputs? (Choose two.)
- A. Kernel indirectly accesses the low memory (LowTotal) through memorypaging
- B. The unit is in kernel conserve mode
- C. The Cached value is always the Active value plus the Inactive value
- D. The unit is running a 32-bit FortiOS
Answer: C,D
NEW QUESTION 37
Examine the output of the 'diagnose ips anomaly list' command shown in the exhibit; then answer the question below.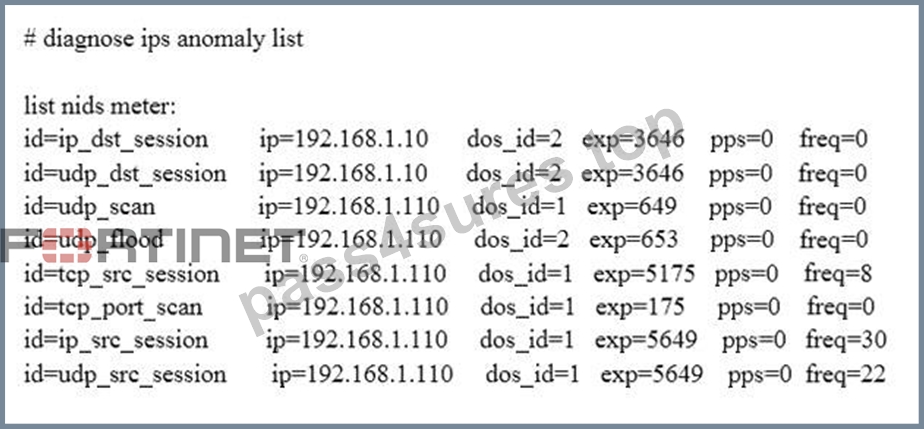
Which IP addresses are included in the output of thiscommand?
- A. Those whose traffic matches an IPS sensor.
- B. Those whose traffic exceeded a threshold of a matching DoS policy.
- C. Those whose traffic was detected as an anomaly by an IPS sensor.
- D. Those whose traffic matches a DoS policy.
Answer: D
NEW QUESTION 38
View the exhibit, which contains a screenshot of some phase-1settings, and then answer the question below.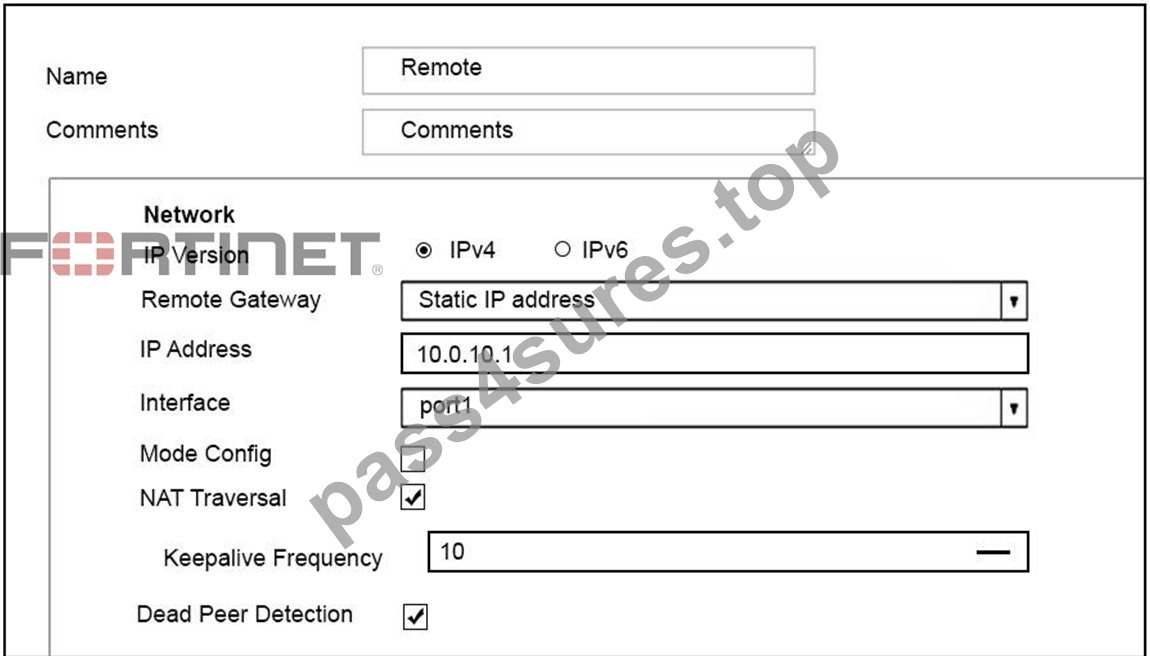
The VPN is up, and DPD packets are being exchanged between both IPsec gateways; however, traffic cannot pass through the tunnel. To diagnose, the administrator enters these CLI commands: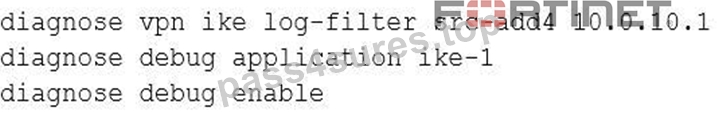
However, the IKE real time debug does not show any output. Why?
- A. The debug output shows phases 1 and 2 negotiations only. Once the tunnel is up, it does not show any more output.
- B. The debug output shows phase 1 negotiation only. After that, the administrator must enable the following real time debug: diagnose debug application ipsec -1.
- C. The log-filter setting was set incorrectly. The VPN's traffic does not match thisfilter.
- D. The debug shows only error messages. If there is no output, then the tunnel is operating normally.
Answer: C
NEW QUESTION 39
An administrator added the following Ipsec VPN to a FortiGate configuration:
configvpn ipsec phasel -interface
edit"RemoteSite"
set type dynamic
set interface "portl"
set mode main
set psksecret ENC LCVkCiK2E2PhVUzZe
next
end
config vpn ipsec phase2-interface
edit "RemoteSite"
set phasel name "RemoteSite"
set proposal 3des-sha256
next
end
However, the phase 1 negotiation is failing. The administrator executed the IKF real time debug while attempting the Ipsec connection. The output is shown in the exhibit.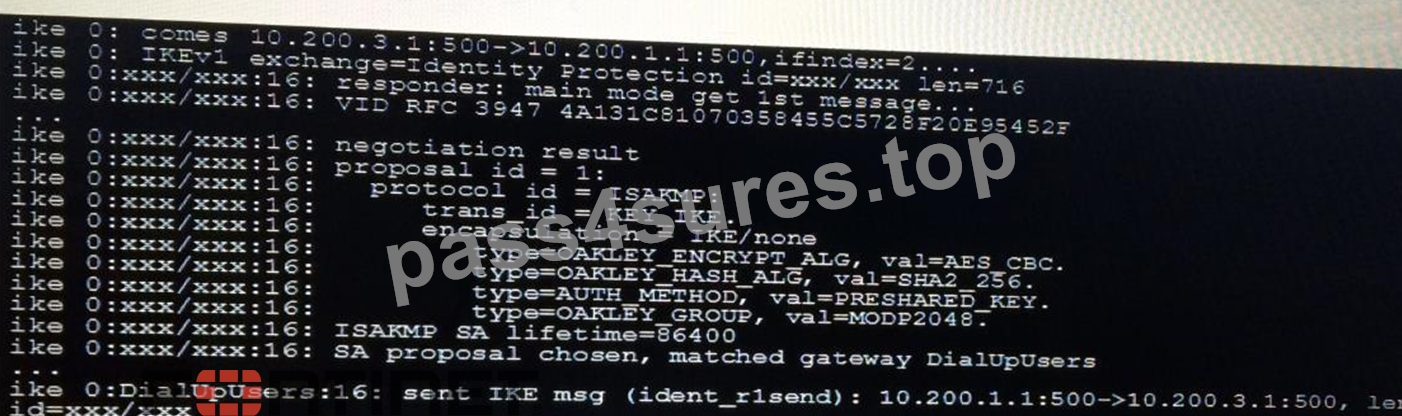
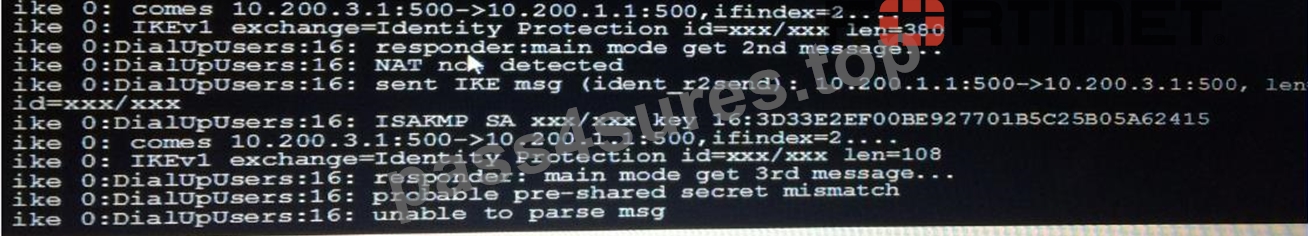
What is causing the IPsec problem in the phase 1 ?
- A. The incoming IPsec connection is matching the wrongVPN configuration
- B. NAT-T settings do not match
- C. The pre-shared key is wrong
- D. The phrase-1 mode must be changed to aggressive
Answer: C
NEW QUESTION 40
Examine the output of the 'get router info ospf interface' command shown in the exhibit; then answer the question below.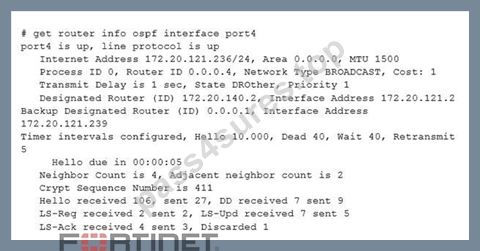
Which statements are true regarding the above output? (Choose two.)
- A. Two OSPF routers are down in the port4 network.
- B. Theport4 interface is connected to the OSPF backbone area.
- C. There are at least 5 OSPF routers connected to the port4 network.
- D. The local FortiGate has been elected as the OSPF backup designated router.
Answer: B,C
Explanation:
Explanation
on BROADCAST network there are 4 neighbors, among which 1*DR +1*BDR. So our FG has 4 neighbors, but create adjacency only with 2 (with DR and BDR). 2 neighbors DRother (not down).
NEW QUESTION 41
Refer to exhibit, which contains the output of a BGP debug command.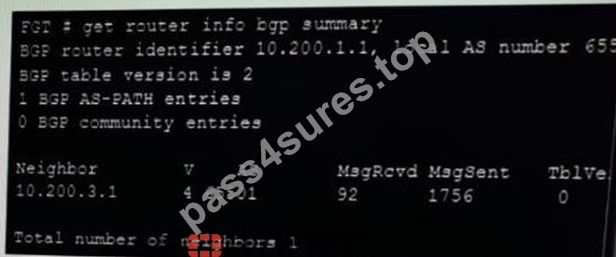
Which statement explains why the state of the 10.200.3.1 peer is Connect?
- A. The local router has received the BGP prefixes from the remote peer.
- B. The local router is receiving the BGP keepalives from the peer, but it has not received a BGP prefix yet.
- C. The TCP session to 10.200.3.1 has not completed the 3-way handshake.
- D. The local router is receiving BGP keepalives from theremote peer, but the local peer has not received the OpenConfirm yet.
Answer: C
Explanation:
Explanation
BGP neighbor states and how they change:* Idle: Initial state* Connect: Waiting for a successful three-way TCP connection* Active: Unable to establish the TCP session* OpenSent: Waiting for an OPEN message from the peer* OpenConfirm: Waiting for the keepalive message from the peer* Established: Peers have successfully exchanged OPEN and keepalive messages
NEW QUESTION 42
Examine the following routing table and BGP configuration; then answer the question below.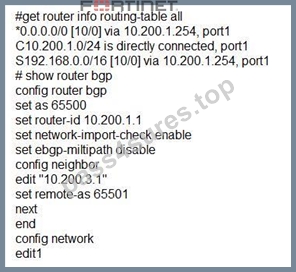
TheBGP connection is up, but the local peer is NOT advertising the prefix192.168.1.0/24. Which configuration change will make the local peer advertise this prefix?
- A. Disable the settingnetwork-import-check.
- B. Enable the redistribution of connected routers into BGP.
- C. Enable the redistribution of static routers into BGP.
- D. Enable the setting ebgp-multipath.
Answer: A
NEW QUESTION 43
An administrator has configured the following CLIscript on FortiManager, which failed to apply any changes to the managed device after being executed.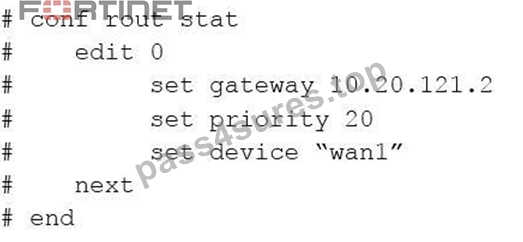
Why didn't the script make any changes to the managed device?
- A. Incomplete commands are ignored in CLI scripts.
- B. Commands that start with the # sign are not executed.
- C. CLI scripts will add objectsonly if they are referenced by policies.
- D. Static routes can only be added using TCL scripts.
Answer: B
Explanation:
Explanation
https://help.fortinet.com/fmgr/50hlp/56/5-6-2/FortiManager_Admin_Guide/1000_Device%20Manager/2400_Scr A sequence of FortiGate CLI commands, as you would type them at the command line. A comment line starts with the number sign (#). A comment line will not be executed.
NEW QUESTION 44
View the following FortiGate configuration.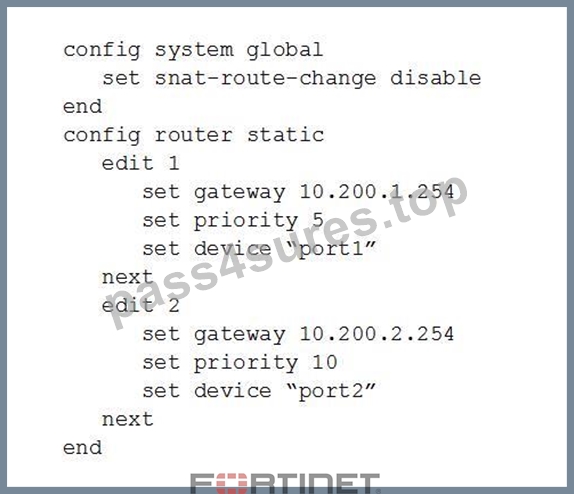
All traffic to theInternet currently egresses from port1. The exhibit shows partial session information for Internet traffic from a user on the internal network: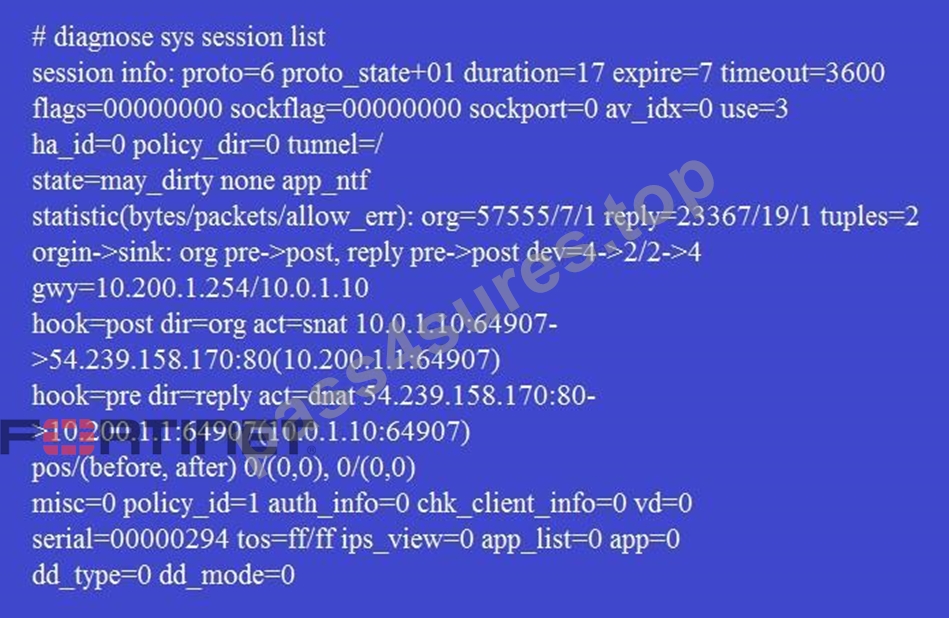
If the priority on route ID 1 were changed from 5 to 20, what would happen to traffic matching that user's session?
- A. The session would be deleted, so the client would need to start a new session.
- B. The session would remain in thesession table, and its traffic would start to egress from port2.
- C. The session would remain in the session table, but its traffic would now egress from both port1 and port2.
- D. The session would remain in the session table, and its traffic would still egress from port1.
Answer: D
Explanation:
Explanation
http://kb.fortinet.com/kb/documentLink.do?externalID=FD40943
NEW QUESTION 45
Examine thefollowing partial outputs from two routing debug commands; then answer the question below: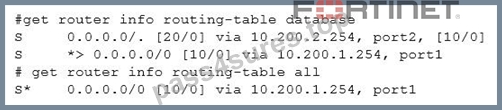
Why the default route using port2 is not displayed in the output of the second command?
- A. It hasa higher priority than the default route using port1.
- B. It is disabled in the FortiGate configuration.
- C. It has a higher distance than the default route using port1.
- D. It has a lower priority than the default route using port1.
Answer: C
Explanation:
Explanation
http://kb.fortinet.com/kb/viewContent.do?externalId=FD32103
NEW QUESTION 46
Which statement about memory conserve mode is true?
- A. A FortiGate starts dropping new sessions when the configured memory use threshold reaches red
- B. A FortiGate enters conserve mode when the configured memory use threshold reaches red
- C. A FortiGate starts dropping all the new and old sessions when the configured memory use threshold reaches extreme.
- D. A FortiGate exits conserve mode when the configured memory use threshold reaches yellow.
Answer: A
NEW QUESTION 47
Examine the output of the 'diagnose debug rating' command shown in the exhibit; then answer the question below.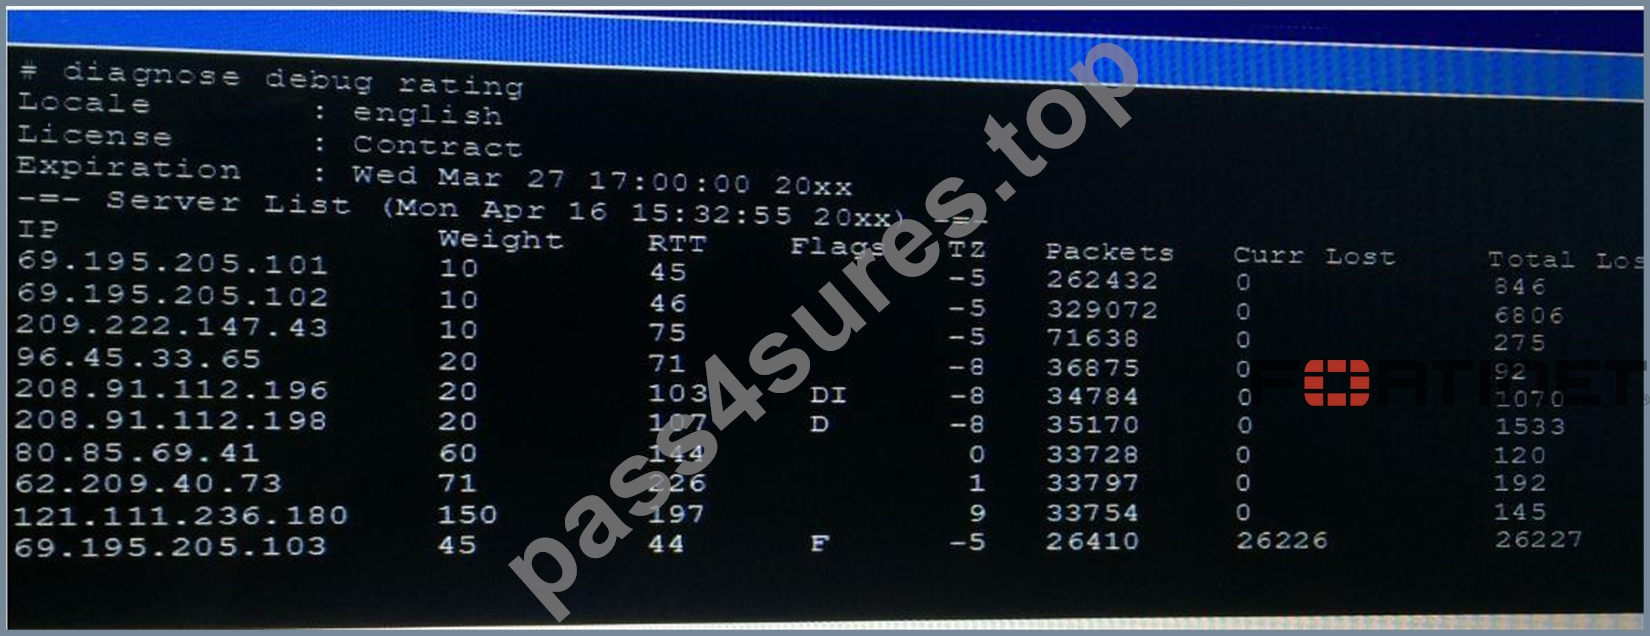
Which statement are true regarding the output in the exhibit? (Choose two.)
- A. There are three FortiGuard serversthat are not responding to the queries sent by the FortiGate.
- B. FortiGate will send the FortiGuard queries to the server withhighest weight.
- C. The TZ value represents the delta between each FortiGuard server's time zone and the FortiGate's time zone.
- D. A server's round trip delay (RTT) is not used to calculate its weight.
Answer: B,C
NEW QUESTION 48
......
How much Fortinet NSE7_EFQ-6.4: Fortinet NSE 7 - Enterprise Firewall 6.4 Exam Cost
The Fortinet NSE7_EFQ-6.4: Fortinet NSE 7 - Enterprise Firewall 6.4 Exam Costs USD 400. As the exam costs may vary country or region vise, it is always recommended to check the official website to see what’s the cost of the exam for your country. The total cost for preparing for the exam will include study materials as well as NSE7 EFW-6.4 dumps and NSE7 EFW-6.4 practice exams. Refer to the official website by clicking here for more info on pricing.
NSE7_EFW-6.4 Actual Questions Answers PDF 100% Cover Real Exam Questions: https://www.pass4sures.top/NSE-7-Network-Security-Architect/NSE7_EFW-6.4-testking-braindumps.html